
Improve security and risk posture.
Remediating vulnerabilities by hand, repository by repository, leaves risk open longer than it needs to be and slows every compliance deadline behind it.
AI has made finding and exploiting vulnerabilities much easier. An attacker needs one, while a defender has to cover the whole estate. An AI-only defense does not scale with the size of the codebase, and it cannot show you that the remediation was complete.
Agents find vulnerabilities faster than teams can fix
them, so Moderne makes the fix deterministic and
estate-wide.
An agent writes a recipe for a brand new vulnerability, and Moderne lands the fix in every affected repository at once.
Mythos found a vulnerability and security flagged it as a V1. Engineers used Moderne to find the blast radius and what it impacts across LOBs then used Claude to build a recipe to fix it. After the analysis from LSTs/Moderne it was downgraded to a V3. This got a lot of attention and kudos from engineering leaders.
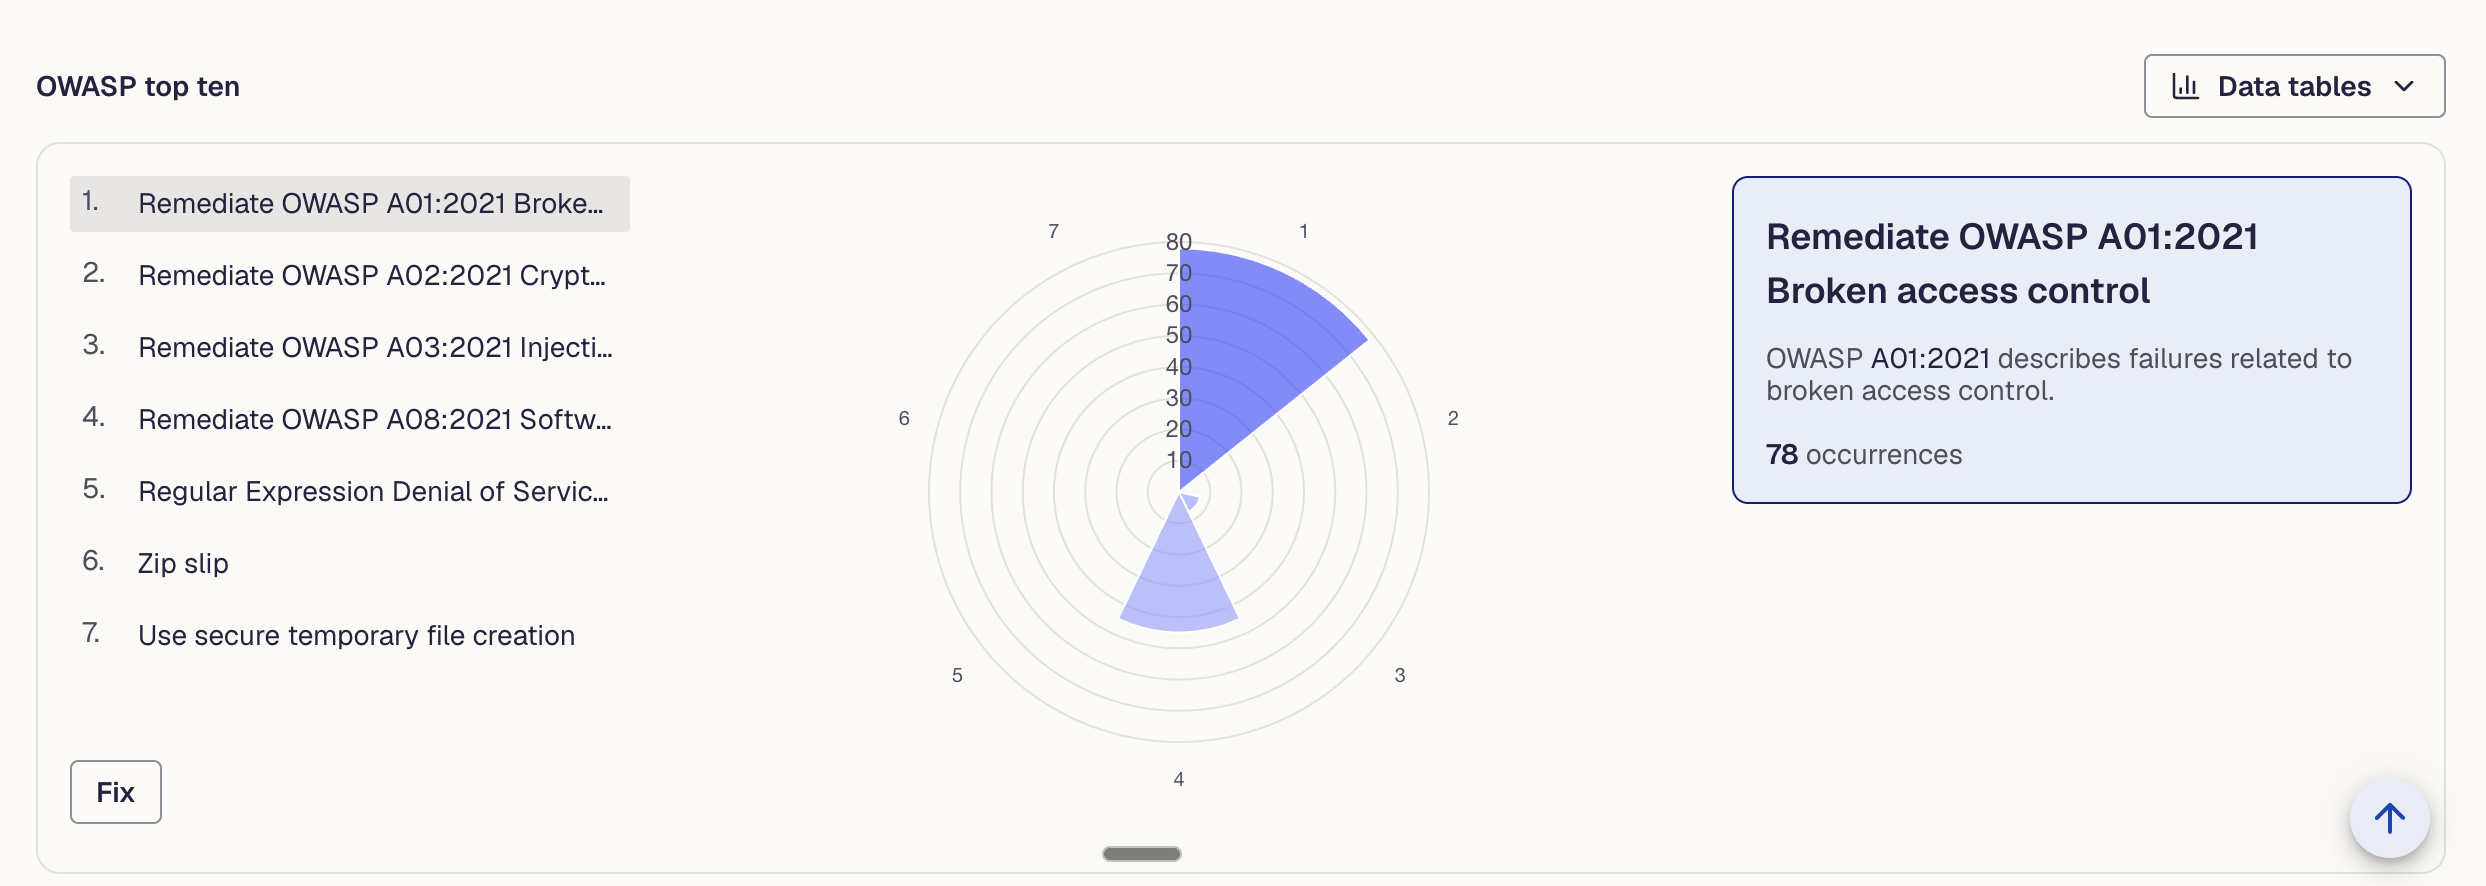
OWASP Top Ten, tracking and remediation in one place.
The security card tracks the vulnerability classes your organization cares about, such as the OWASP Top Ten, and determines the number of occurrences across every repository. Select an issue to see how many remain. Press Fix to run the remediation recipe, review the diffs, and commit. The data tables show which repositories and files each occurrence came from.
Recipes
- Find and fix vulnerable Maven/Gradle dependenciesKnown CVEs matched against the dependency graph, then upgraded to a fixed version.
- Remediate OWASP A01:2025 Broken access controlThe 2025 list. Recipes ship for A01 through A08.
- Post quantum cryptographyTLS configuration and key exchange audited and moved to post-quantum ready settings.
- Find and fix vulnerable npm dependenciesKnown CVEs matched against the npm dependency graph, then upgraded.
- Remove redundant dependency overridesOverrides that no longer change the resolved version, removed.
- Find end-of-life npm dependenciesPackages past their support window, surfaced across the estate.
- Find and fix vulnerable NuGet dependenciesKnown CVEs matched against the NuGet dependency graph, then upgraded.
- Find end-of-life NuGet dependenciesPackages past their support window, surfaced across the estate.
- Upgrade C# dependency versionsDependency references moved to a chosen target across every project file.
- Apply Docker security best practicesRoot users, secrets in layers, and unpinned base images addressed across Dockerfiles.
- Kubernetes best practicesManifest hygiene covering security context, resource limits, and probes.
- Best practices for AWSTerraform AWS configuration checked against encryption, access, and logging baselines.
Case studies in a stronger security posture
Find the vulnerability once. Remediate everywhere it actually reaches.