
Four ways to fix security vulnerabilities across every repository
Contents
- 1. Code analysis finds exposed secrets and insecure APIs.
- 2. Static analysis with automated fixes repairs weaknesses in your own code.
- 3. Software composition analysis with automated upgrades fixes vulnerable dependencies.
- 4. Automated migrations remove vulnerabilities a version bump can’t.
- Agent-written code needs the same checks.
- How do you prevent new vulnerabilities from entering the codebase?
- Moderne keeps your code under your control.
Finding a vulnerability is the start of the work. Fixing it in every repository where it appears takes far longer, and that’s where security backlogs grow. Moderne closes the gap between finding and fixing with OpenRewrite recipes that find and fix vulnerabilities across all of an organization’s code at once.
The gap is already wide. Veracode’s 2025 State of Software Security report found that the average time to fix a security flaw rose from 171 days to 252 days over five years. It gets harder to close as AI models find flaws faster.
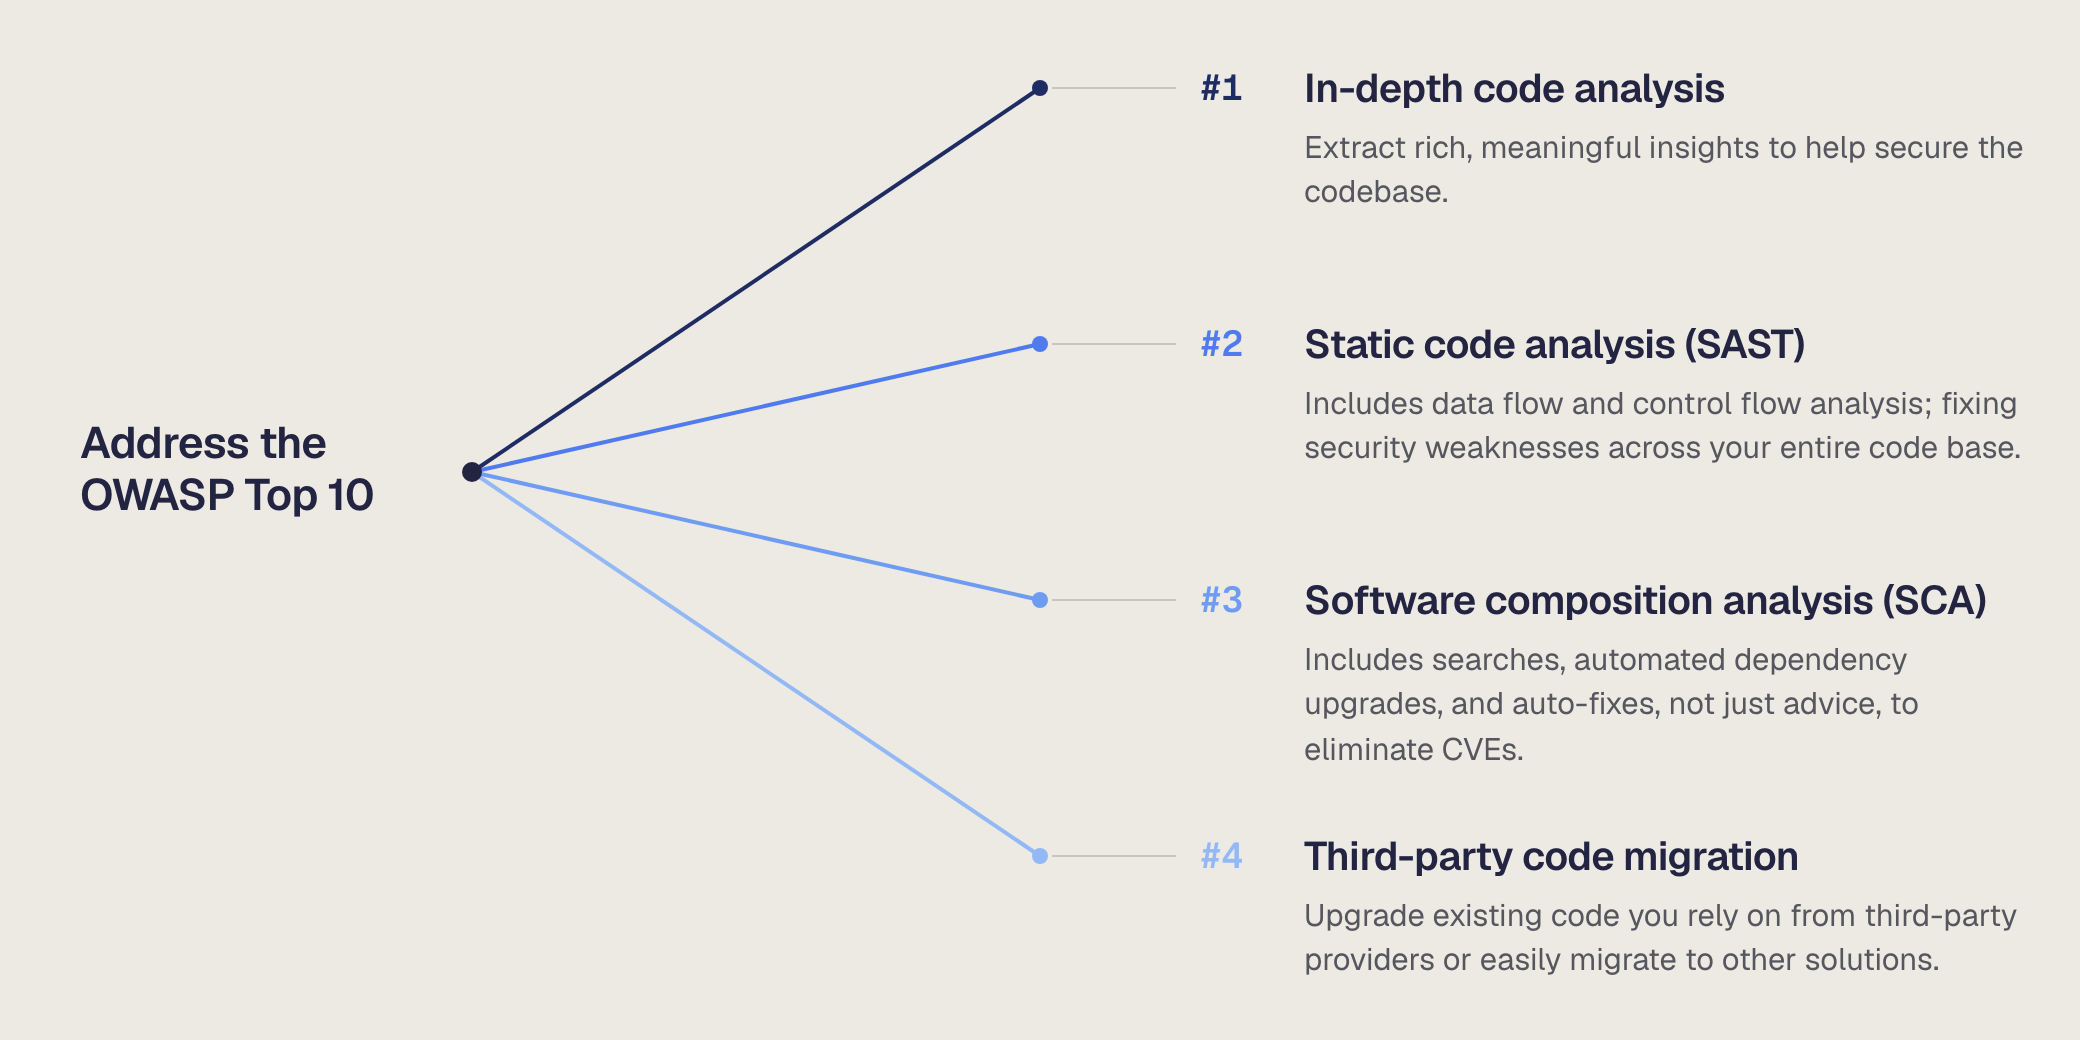
Moderne works on it in four places, from exposed secrets to framework migrations. Together they cover both layers of the stack: the code your teams write and the supply chain it depends on. For the step-by-step version, read the playbook for secure code at scale.
1. Code analysis finds exposed secrets and insecure APIs.
Moderne can search every repository for the places where data leaves an application or secrets sit in the open, including code that comes in through direct and transitive dependencies. Security teams usually can’t see into a large codebase that way without an expert digging through it by hand.
The Find Spring API endpoints recipe lists every HTTP endpoint an application exposes, so a team can assess what’s reachable. Find sensitive API endpoints narrows that to data models that expose PII or secrets, which this post covers in detail. Find secrets looks for credentials stored in plain text, with detectors for 28 kinds of secrets from AWS, GitHub, Stripe, and other services.
2. Static analysis with automated fixes repairs weaknesses in your own code.
Moderne’s static analysis finds security weaknesses in the code a team writes, and then fixes them. Developers review and merge the change instead of working out the fix themselves.
The analysis follows both control flow and data flow. Data flow, or taint analysis, tracks how untrusted values move through a program, which is how injection and encoding problems are found. This post on overlapping taint sources explains how Moderne tells a real risk from a harmless use.
Examples of fixes Moderne applies:
-
Common static analysis issues: fixes the findings traditional SAST tools report most, in the code’s existing style
-
OWASP Top Ten: remediates vulnerabilities from the OWASP Top Ten, such as broken access control, cryptographic failures, and security misconfigurations
-
Partial path traversal vulnerability: fixes code to prevent a common directory traversal attack
-
Zip slip: adds path checks so a malicious archive can’t overwrite files outside its target directory
-
Enable CSRF attack prevention: turns on Spring’s protection against cross-site request forgery
3. Software composition analysis with automated upgrades fixes vulnerable dependencies.
Moderne checks every direct and transitive dependency in every repository against the GitHub Advisory Database, then fixes what it can. That matters because much of an application is code its team didn’t write, and open source dependencies change on their own schedules. The Find and fix vulnerable dependencies recipe starts with patch upgrades, which aren’t supposed to break anything, and can override vulnerable transitive versions. Its data table lists every remaining vulnerability with the version that fixes it. The same check runs on npm and NuGet dependencies, along with recipes that surface packages past end of life. Dockerfile recipes cover the container base images underneath. Manage your software dependencies or they will manage you walks through the full flow, and the docs how-to covers the options.
A version bump often isn’t enough. In one analysis, 70% of vulnerable dependencies needed a minor or major upgrade or had no fix available (Dependency updates unmasked), and those upgrades can break code. That’s where the migrations in the next section come in.
Two more recipes help around the edges. Exclude Maven dependency removes a vulnerable transitive dependency that can’t be patched and isn’t needed at runtime, and Find licenses in use in third-party dependencies reports every license in the codebase for compliance or due diligence.
4. Automated migrations remove vulnerabilities a version bump can’t.
Some vulnerabilities only close with a move to a newer framework or library, and those moves change application code. A major framework migration usually brings a chain of dependency changes with it, which is why teams put them off until a vulnerability forces the issue.
Recipes make those migrations routine. A global financial services company runs its Spring Boot and Java migrations and its vulnerability fixes as recipes in its existing pipelines. It now fixes more than 100 critical security issues in a single CI/CD run. Migrations that remove known vulnerabilities include:
-
Spring Boot 4.0: upgrades build files, deprecated APIs, and configuration, and chains the Spring Framework and Spring Security migrations (see the Spring Boot 4 migration guide)
-
Java 25: replaces deprecated APIs and updates build files and plugins
-
Log4j to SLF4J: moves logging calls from the Log4j API to SLF4J
-
Marshalling: secures Jackson default typing, SnakeYAML constructors, and JMS deserialization against malicious input
-
Post-quantum cryptography: audits TLS configuration and key exchange and moves them to post-quantum ready settings
When the fix is in a major version a team can’t take yet, a backpatch applies the security fix to the version it’s on.
Agent-written code needs the same checks.
Keeping new vulnerabilities out means running the same checks on every change, including the ones a coding agent writes. Agents can use the fixes too: Claude Code or Copilot can call the same recipes through Moderne instead of writing a fix by hand.
Agents can also write the recipe for a brand-new vulnerability. When an AI model finds a new flaw, an agent working with Moderne can turn that finding into a deterministic recipe, and Moderne runs it across every affected repository at once, so the fix reaches everywhere the vulnerability does.
The State of AppSec in the Era of AI [Panel]
▶ Watch on YouTube
How do you prevent new vulnerabilities from entering the codebase?
Run the same deterministic checks on every change. That means type-aware searches for known-bad patterns, dependency checks that include transitive dependencies, and recipes that fix a finding in the same pull request. The first run fixes the backlog, and later runs on each change keep it from coming back.
Moderne keeps your code under your control.
Your code is never exposed to anyone outside your organization. Moderne holds SOC 2 Type 2 certification and runs as a single-tenant hybrid-cloud SaaS deployment. For teams that can’t use a SaaS platform, Moderne DX runs fully air-gapped, and the Moderne CLI runs recipes locally.
Operations follow your company’s security controls. Authentication runs through your SSO, and authorization matches the access developers already have in your source control system. You manage encryption with your own keys. Your source code stays in your environment, and an on-premises, egress-only agent tunnels all communication to your single-tenant SaaS.
To see security recipes run on open source code, try the Moderne Platform, or book a demo to see them on your own repositories.
Originally published